A promising enterprise deal has reached final procurement. Your customer likes the product, the pricing is agreed upon, and implementation discussions are underway. That’s when the security questionnaire arrives. What the buyer wants is evidence of SOC 2 or ISO 27001 compliance.
That request can decide which security project deserves attention first for an Australian software company entering enterprise markets. If you choose incorrectly, you may spend months preparing evidence that doesn’t meet the customer’s requirements.
Rather than scrambling, use the security questionnaire as a prompt to plan. Knowing what the customer actually needs, and by when, narrows the options quickly.
Read the Customer’s Requirement Before You Choose
The SOC 2 vs ISO 27001 decision shouldn’t begin with whichever framework appears easier to achieve. Begin with the customer’s contract or security requirements. Where Australian and European enterprise buyers commonly recognize ISO 27001, North American SaaS customers frequently ask for SOC 2 reports.
These preferences aren’t universal. Some customers accept either framework, while others specify one. When a contract explicitly requires SOC 2, you can’t assume an ISO 27001 certificate will be accepted instead. Check with the buyer whether equivalent assurance would satisfy the requirement before you commit resources.
Certification and Attestation Are Different
What your business receives after the independent assessment is one important distinction in the ISO 27001 vs SOC 2 comparison. ISO 27001 is an international standard for information security management systems. An accredited certification body assesses the organization and can issue a certificate valid for three years, subject to ongoing surveillance audits. SOC 2 isn’t the same.
A licensed CPA firm issues an attestation report after examining controls against the AICPA Trust Services Criteria. At a particular point in time, controls are evaluated in a SOC 2 Type 1 report. Type 2 also assesses how effectively they operate over a defined period. No formal SOC 2 certification exists. What customers receive is an auditor’s report, not an ISO-style certificate.
You’ll need to keep that difference in mind when describing your status to customers. Wording gets noticed by procurement teams, so be precise about whether you hold a certificate or a report.
How the Two Frameworks Overlap
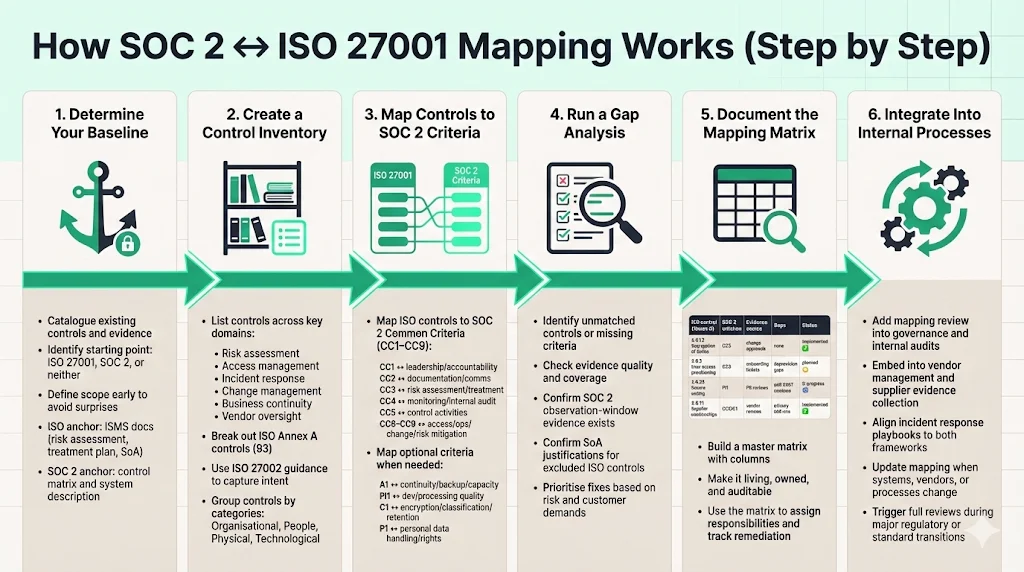
The SOC2 vs ISO 27001 discussion tends to overlook how much operational work the two frameworks have in common. Security practices such as access management, risk assessment, incident response, supplier oversight, and change management feature in both.
Picture a SaaS company that already keeps employee access records, documents security incidents, and reviews important suppliers. Much of this evidence may support both assessments, although the requirements and testing methods differ. Organizations planning to pursue both frameworks can map shared controls early and avoid maintaining completely separate evidence collections.
For many businesses, establishing an ISO 27001 information security management system first provides a useful foundation for subsequent SOC 2 preparation.
It’s still necessary to check each control against the criteria of the framework being assessed. What satisfies one standard may need extra evidence or a different test to satisfy the other.
Don’t Overlook the Time an Audit Takes
Audit readiness isn’t simply a matter of writing policies. Security controls need to be implemented, responsibilities assigned, and evidence collected. Structured compliance support is offered to Australian businesses by Siege Cyber, with programs designed to achieve audit readiness in approximately three to nine months.
Before the independent auditor can issue a SOC 2 Type 2 report, an additional observation period may be required. How long it takes depends on the scope, existing controls, and evidence requirements. Budgets should also cover independent certification and attestation fees.
Staff time is a cost as well, because people will be involved in gathering evidence and answering auditor questions. Agreeing the scope early, including which systems and services are covered, helps keep the timeline and the budget realistic.
Compliance That Helps Beyond the Sales Process
Improving security operations, and not only satisfying a customer questionnaire, is what a well-designed compliance program should do. Regular access reviews, incident response exercises, employee training, and technical testing help organizations spot weaknesses and manage risks more consistently.
Fixed-price compliance support, Australian-based specialists, and penetration testing are provided within Siege Cyber’s compliance packages.
Businesses comparing ISO 27001 SOC 2 requirements can draw on this support when assessing existing controls, identifying gaps, and preparing for independent assessment.
Choose the Framework That Serves Your Business Goals
SOC 2 should come first if it’s what your immediate opportunity requires. Where your customers mainly operate in Australia or Europe, ISO 27001 may make the more practical starting point. A coordinated approach can reduce duplicated preparation when both markets matter.
Confirm what your customers will accept, define the systems covered by the assessment, and understand the complete timeline and cost before investing. What makes a framework right is that it meets your business obligations while helping establish security practices your team can maintain.